A clearer view of project security
Use Basic and Deep scans to find project issues, understand who can fix them, and review the corrected version before it goes live.
Useful security feedback tells you what to do next
A membership site can look finished before its access rules are right. The pages load, the sign-in form works, and the member area contains the expected information. The question that remains is whether one member can see something intended for another.
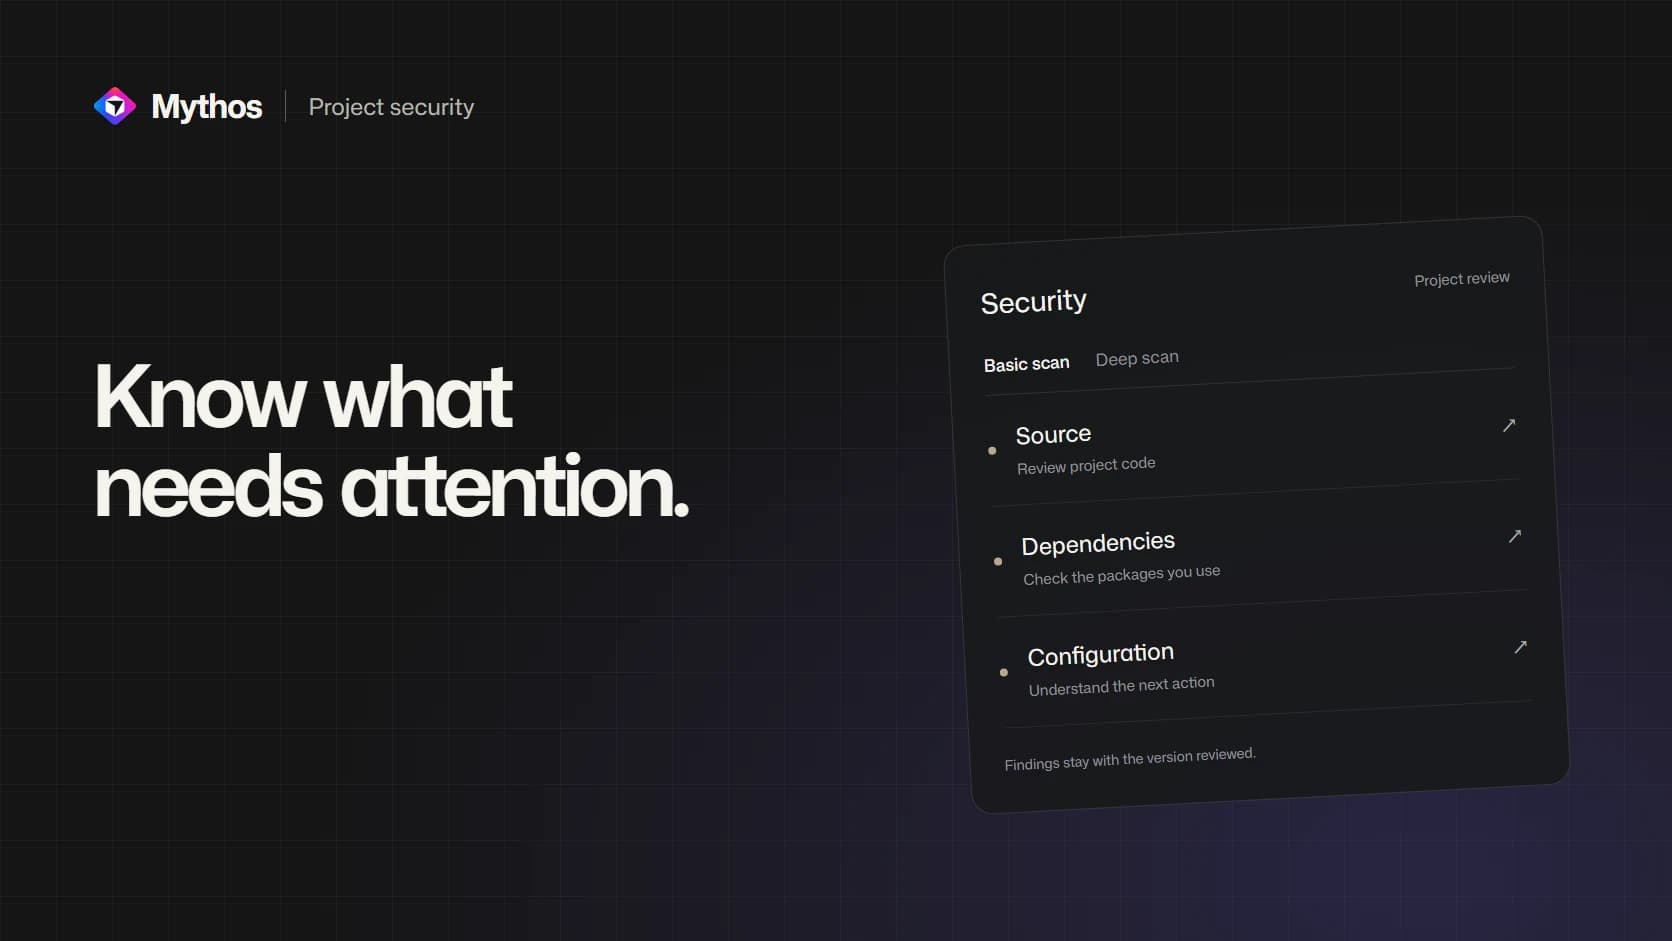
Mythos's Security view gives project administrators a place to review findings alongside the project they are building. Each useful finding needs a location, an explanation and a next action. That makes it possible to investigate a specific problem instead of adding a vague request to make the whole app secure.
Open More → Security to review the available scans and existing results.
Basic and Deep answer different questions
Basic checks cover source-level concerns such as possible exposed secrets, dependencies and configuration guidance. Where an attached managed backend is accessible, database advisor checks can contribute findings too. Deep adds a review of the project's application code.
Read the coverage and version information with the results. A review of yesterday's source may not describe today's app, and a check that could not run cannot tell you that its area is clear. The panel identifies stale results and incomplete coverage so you can see that distinction.
Running a scan gathers findings. It does not by itself rewrite the app. The Security documentation explains the controls and how to interpret the review.
Follow the finding to the right place
Some findings call for a change in your project. Others need action on a connection or concern a dependency managed by Mythos. The suggested action owner helps you avoid trying to solve every problem by changing a page.
For the membership example, a project-code finding might lead to a focused request to enforce the intended access rule. After the change, test with separate accounts: the owner of a record, another member and a signed-out visitor. The permitted person should still complete the task, while the other two should not receive the protected information.
A useful fix preserves both sides of that behavior. Hiding a link is not enough if the information remains accessible through another route; blocking every user would break the feature.
Published